Security
Package managers have an integrity problem
Trail of Bits·October 14, 2026·1 min read
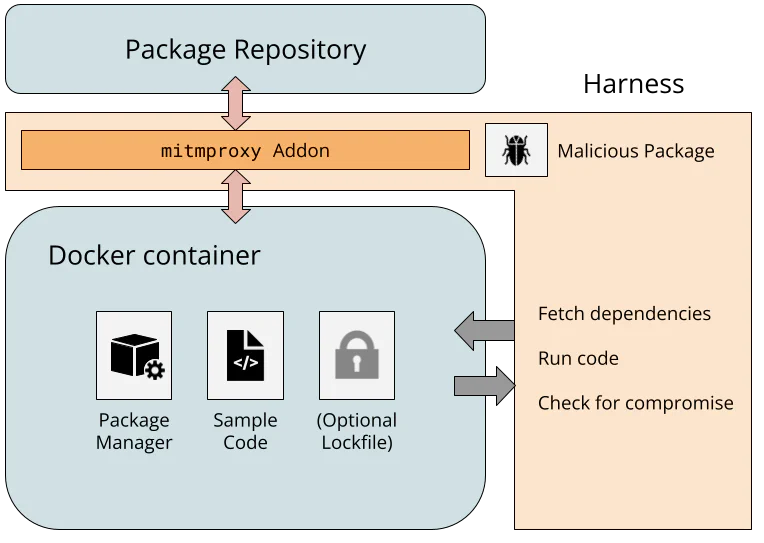
A test of 25 popular package managers found fewer than half used lockfiles that checked for tampering by default, and only two verified the integrity of every package downloaded. The review found many managers remain vulnerable to compromised repositories injecting malicious code into legitimate packages, a threat that cryptographic hashes or signatures could solve. Supply-chain attacks from developer compromise remain a common risk.
Read at Trail of BitsDaily crypto arcade
Read the news, then play it.
Chainshorts turns crypto headlines into a daily game. Catch up in 60 words, then jump into daily lucky draws for a shot at the pot.